
Salesforce, the software company behind one of the best CRMs for sales, has released out a patch for its email services after security researchers discovered a zero-day vulnerability that allowed cyber criminals to target Facebook users with a convincing phishing scam.
The actively exploited bug was discovered by the team at Guardio Labs and has been dubbed “PhishForce”. It made use of a flaw in Salesforce’s “email-to-case” feature – which lets users automate the creation of tickets for customer queries – to send outbound emails purporting to be from Meta Platforms via the official “@case.salesforce.com” domain.
Not only did these emails look genuine to the recipients, but they evaded Facebook’s built-in phishing detection defenses as well, once again highlighting how even the most robust antivirus software and related solutions can be duped by gaps in the security architecture of popular products.
How the Salesforce Phishing Attack Worked
The phony phishing emails were titled “Breach of Content Standards” and claimed to advise recipients of an account compromise and impending suspension due to “suspicions of impersonation” on their social media account. Which of course is wildly ironic and proof that cyber criminals are nothing if not a humorous bunch.

This just in! View the top business tech deals for 2026 👨💻
In order to avoid the “suspension”, users were directed to a fake “support” page, at which point they were asked to input sensitive information. While the Guardio Labs report makes clear the campaign is known to have operated successfully, it’s not clear how many people actually fell victim to it.
Adding a further air of authenticity to the ruse, the emails were addressed to the target’s real name, which also helped the messages bypass Facebook’s anti-spam and anti-phishing filters.
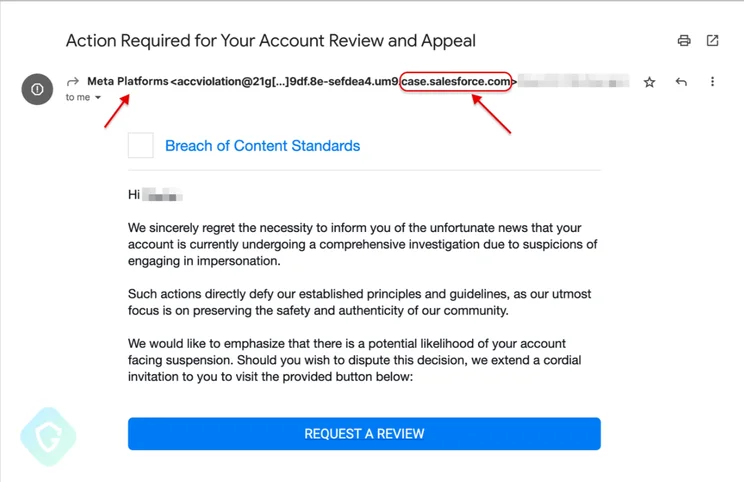
Image credit: Guardio Labs
Salesforce Dreaming Big Despite Layoffs
Guardio Labs also notes that Salesforce acted quickly to address the vulnerability: it was reported to the company on July 28th and a patch was released the same day. The security researchers also say they advised Facebook owner Meta of the hole in its systems, which seemed to be related to legacy features on “apps.facebook.com.”
News of the security flaw comes as Salesforce enters an important couple of months as a company and as a brand. Specifically, the popular CRM maker is in the midst of a number of new launches ahead of its annual Dreamforce 2023 conference in September. These include the suite of new AI features being brought to its core products, while subsidiary Slack has also just unveiled a sales-specific edition as it looks to diversify its offering.
At the same time, Salesforce pricing is increasing for the first time in a number of years and the company hasn’t found itself immune to the wave of tech layoffs sweeping the industry, either. For its part, Meta finds itself in the eye of the social media storm as ever, launching its new app Threads as an alternative to Twitter (now X).


